Microsoft - MD-102: Managing and Securing Microsoft 365 Endpoints by using Intune
Sample Questions
Question: 479
Measured Skill: Optimize endpoint operations by using automation, monitoring, and reporting (10–15%)
You have a Microsoft 365 subscription that uses Microsoft Security Copilot in Intune. The subscription contains 1,000 Windows 11 devices that are onboarded to Microsoft Defender for Endpoint P2.
A Defender report identifies newly exposed managed devices.
You need to generate a set of prioritized findings for the exposed devices. The solution must include details about the affected devices and the potential impact of the exposure.
Which Security Copilot agent should you use?| A | Policy Configuration Agent |
| B | Vulnerability Remediation Agent |
| C | Device Offboarding Agent |
| D | Change Review Agent |
Correct answer: BExplanation:
The Vulnerability Remediation Agent in Microsoft Security Copilot helps security and IT administrators identify, prioritize, and remediate vulnerabilities affecting managed devices.
The agent uses vulnerability information from Microsoft Defender for Endpoint and device management information from Microsoft Intune.
It can help administrators:
- Identify exposed devices: Determine which managed devices are affected by newly discovered vulnerabilities.
- Prioritize findings: Evaluate vulnerabilities based on severity, exposure, and potential impact.
- Assess potential impact: Provide context about affected devices and the risks associated with identified vulnerabilities.
- Recommend remediation: Identify appropriate actions to reduce exposure, such as updating vulnerable applications.
This directly addresses the requirement to generate prioritized findings that include affected device information and potential exposure impact.
References:
Microsoft Copilot in Intune
Vulnerability Remediation Agent in Microsoft Intune
Question: 480
Measured Skill: Optimize endpoint operations by using automation, monitoring, and reporting (10–15%)
You have a Microsoft 365 subscription that uses Microsoft Security Copilot in Intune. The subscription has Multi Admin Approval enabled for PowerShell scripts.
A pending approval request contains a PowerShell script that modifies the local Administrators group membership on Windows devices.
You need to ensure that approvers use a recommendation that considers contextual risk signals from identity, device management, and vulnerability data before approving privileged changes.
Which Security Copilot agent should you use?| A | Device Offboarding Agent |
| B | Vulnerability Remediation Agent |
| C | Policy Configuration Agent |
| D | Change Review Agent |
Correct answer: DExplanation:
The Change Review Agent in Microsoft Security Copilot helps administrators evaluate proposed changes in Microsoft Intune before approving them.
It supports Multi Admin Approval (MAA) workflows by providing contextual risk assessments and recommendations.
For a PowerShell script that modifies the local Administrators group membership, the agent can help approvers evaluate:
- Identity risks: Security implications of granting or modifying administrative privileges.
- Device management context: Information about affected devices and their configurations.
- Vulnerability data: Known security exposures that could increase the risk of the proposed change.
- Potential impact: Security consequences of implementing the requested modification.
The agent uses these signals to provide recommendations that help administrators make informed approval decisions.
References:
Microsoft Copilot in Intune
Change Review Agent overview
Question: 481
Measured Skill: Protect devices (15–20%)
You have a Microsoft 365 subscription that contains devices enrolled in Microsoft Intune.
You need to create Endpoint security policies to enforce the following requirements:
- Computers that run macOS must have FileVault enabled.
- Computers that run Windows 11 must have Microsoft Defender Credential Guard enabled.
Which Endpoint security feature should you use for each requirement?
(To answer, drag the appropriate features to the correct requirements. Each feature may be used once, more than once, or not at all. NOTE: Each correct selection is worth one point.)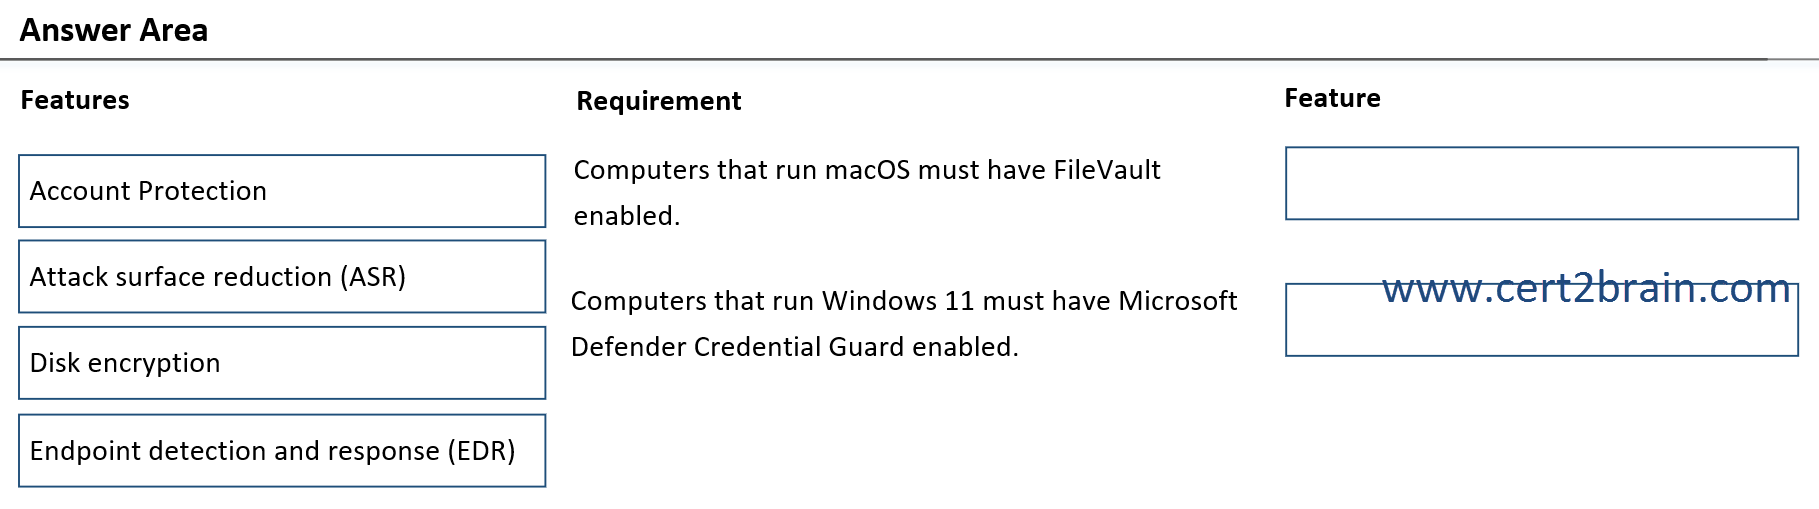
| A | Computers that run macOS must have FileVault enabled: Account Protection
Computers that run Windows 11 must have Microsoft Defender Credential Guard enabled: Disk encryption
|
| B | Computers that run macOS must have FileVault enabled: Attack surface reduction (ASR)
Computers that run Windows 11 must have Microsoft Defender Credential Guard enabled: Endpoint detection and response (EDR) |
| C | Computers that run macOS must have FileVault enabled: Disk encryption
Computers that run Windows 11 must have Microsoft Defender Credential Guard enabled: Account Protection |
| D | Computers that run macOS must have FileVault enabled: Endpoint detection and response (EDR)
Computers that run Windows 11 must have Microsoft Defender Credential Guard enabled: Disk encryption |
| E | Computers that run macOS must have FileVault enabled: Attack surface reduction (ASR)
Computers that run Windows 11 must have Microsoft Defender Credential Guard enabled: Account Protection |
| F | Computers that run macOS must have FileVault enabled: Attack surface reduction (ASR)
Computers that run Windows 11 must have Microsoft Defender Credential Guard enabled: Endpoint detection and response (EDR) |
Correct answer: CExplanation:
macOS → Disk encryption
In Microsoft Intune, FileVault is managed through Endpoint security > Disk encryption. Microsoft specifically lists a FileVault profile for macOS under Disk encryption.
Windows 11 → Account Protection
The Account protection endpoint security policy includes settings designed to protect user credentials, including Microsoft Defender Credential Guard.
References:
Encrypt macOS devices with FileVault using Intune
Account protection policy for endpoint security in Intune
Question: 482
Measured Skill: Optimize endpoint operations by using automation, monitoring, and reporting (10–15%)
You have a Microsoft 365 subscription that contains 1,000 Windows devices enrolled in Microsoft Intune.
The devices send vulnerability data to Microsoft Defender Vulnerability Management.
You need to use Microsoft Security Copilot in Intune to prioritize remediation for exposed devices and retain a record after each remediation is complete.
What should you do?
(To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.)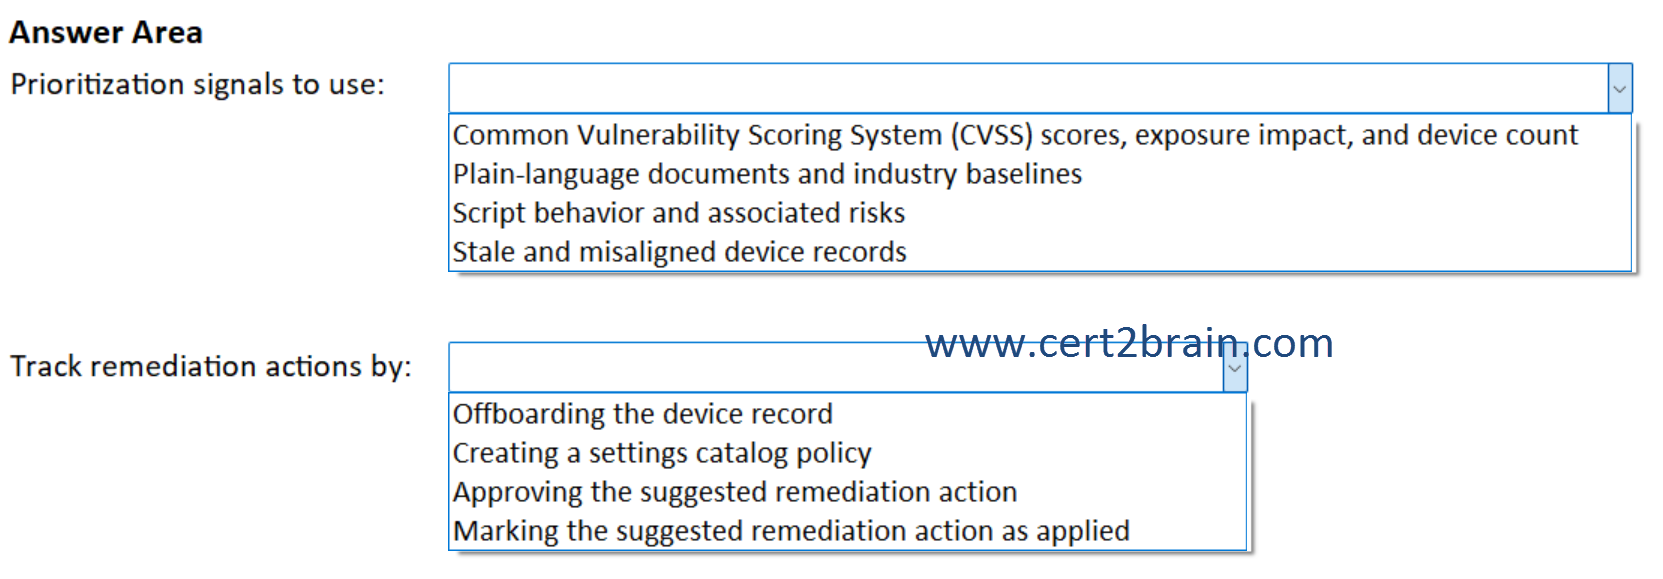
| A | Prioritization signals to use: Common Vulnerability Scoring System (CVSS) scores, exposure impact, and device count
Track remediation actions by: Marking the suggested remediation action as applied |
| B | Prioritization signals to use: Common Vulnerability Scoring System (CVSS) scores, exposure impact, and device count
Track remediation actions by: Creating a settings catalog policy |
| C | Prioritization signals to use: Plain-language documents and industry baselines
Track remediation actions by: Offboarding the device record |
| D | Prioritization signals to use: Script behavior and associated risks
Track remediation actions by: Marking the suggested remediation action as applied |
| E | Prioritization signals to use: Script behavior and associated risks
Track remediation actions by: Creating a settings catalog policy |
| F | Prioritization signals to use: Stale and misaligned device records
Track remediation actions by: Approving the suggested remediation action |
Correct answer: AExplanation:
Prioritization signals to use → Common Vulnerability Scoring System (CVSS) scores, exposure impact, and device count
The Vulnerability Remediation Agent in Microsoft Security Copilot helps administrators prioritize security vulnerabilities affecting Intune-managed devices.
The agent uses vulnerability information from Microsoft Defender Vulnerability Management to evaluate remediation priorities.
Relevant signals include:
- CVSS scores: Indicate the technical severity of identified vulnerabilities.
- Exposure impact: Helps determine how significantly a vulnerability affects the organization's security posture.
- Device count: Identifies how many managed devices are affected by a vulnerability.
Combining these signals helps administrators prioritize vulnerabilities that present the greatest organizational risk.
Track remediation actions by → Marking the suggested remediation action as applied
After completing a remediation, administrators can mark the suggested remediation action as applied.
This helps maintain a record of completed remediation activities.
It also supports tracking remediation progress and distinguishing completed actions from outstanding recommendations.
References:
Use the Vulnerability Remediation Agent
Microsoft Copilot in Intune
Question: 483
Measured Skill: Manage and secure applications (15–20%)
You have 1,000 Windows 11 devices enrolled in Endpoint analytics.
You perform the following actions:
- Apply an Intune data collection policy to all the devices.
- Create a custom baseline named PreUpgrade.
- Update an app named App1.
A week after you perform the actions, users report that device sign-ins are slower, and App1 closes unexpectedly.
You need to analyze endpoint health trends after the App1 update. The solution must meet the following requirements:
- Compare current Endpoint analytics scores to PreUpgrade.
- Normalize application failures by application usage duration.
What should you use?
(To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.)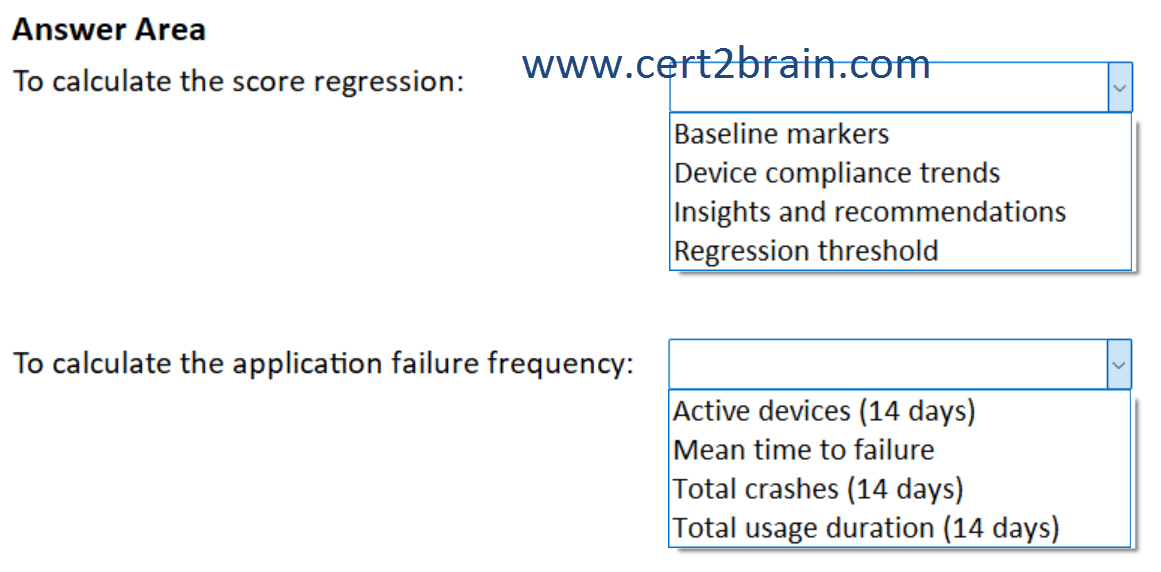
| A | To calculate the score regression: Baseline markers
To calculate the application failure frequency: Active devices (14 days) |
| B | To calculate the score regression: Baseline markers
To calculate the application failure frequency: Mean time to failure |
| C | To calculate the score regression: Device compliance trends
To calculate the application failure frequency: Total crashes (14 days) |
| D | To calculate the score regression: Device compliance trends
To calculate the application failure frequency: Total usage duration (14 days) |
| E | To calculate the score regression: Insights and recommendations
To calculate the application failure frequency: Mean time to failure |
| F | To calculate the score regression: Regression threshold
To calculate the application failure frequency: Total crashes (14 days) |
Correct answer: BExplanation:
To calculate the score regression → Baseline markers
Microsoft Intune Endpoint analytics allows administrators to create custom baselines to compare device performance over time.
In this scenario, the custom baseline PreUpgrade represents the device performance before App1 was updated.
Baseline markers allow you to compare current Endpoint analytics scores against the previously established baseline.
This helps identify:
- Changes in startup performance.
- Decreases in Endpoint analytics scores.
- Performance regressions following application updates.
- Differences between current performance and the PreUpgrade baseline.
To calculate the application failure frequency → Mean time to failure
The Mean time to failure (MTTF) metric measures how long an application runs, on average, before experiencing a failure.
It accounts for application usage duration rather than relying only on the total number of crashes.
For example, consider two applications:
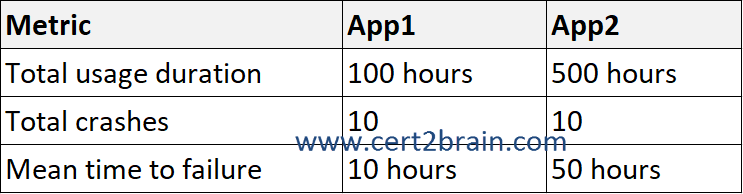
Although both applications experienced 10 crashes, App1 failed more frequently relative to its usage duration.
Therefore, Mean time to failure is the appropriate metric for comparing application reliability.