Microsoft - SC-100: Microsoft Cybersecurity Architect
Sample Questions
Question: 366
Measured Skill: Design security solutions for applications and data (20–25%)
You have a Microsoft Entra tenant that uses Microsoft Entra Private Access.
You plan to publish a group of internal web apps by using a Global Secure Access application.
You need to ensure that users can access the web apps by connecting through the Global Secure Access application.
What should you use?| A | A Conditional Access policy that grants access from only compliant devices. |
| B | A forwarding profile that directs all outbound internet traffic through the Microsoft backbone network. |
| C | A connector group that contains the connectors used to access the web apps and a single endpoint for the internal fully qualified domain names (FQDNs). |
| D | An access policy that limits connections based on user groups. |
Correct answer: CExplanation:
Microsoft Entra Private Access provides secure access to your organization's internal resources by enabling you to control and secure access to specific network destinations on your private network. This allows you to provide granular network access based on user needs. To do this, create an Enterprise application and add the application segment that is used by the internal, private resource that you want to secure. Network requests sent from devices running the Global Secure Access client to the application segment you added to your Enterprise application will be acquired and routed to your internal application by the Global Secure Access cloud service without any ability to connect to other resources on your network. By configuring an Enterprise application, you create per-app access to your internal resources. Enterprise applications provide you a segmented, granular ability to manage how your resources are accessed on a per-app basis.
When publishing internal web applications with Microsoft Entra Private Access and a Global Secure Access application, you must configure:
- A connector group that contains one or more active Microsoft Entra private network connectors.
- Application segments/endpoints that define the internal FQDNs (or IP addresses) of the web applications.
- The connector group routes traffic from the Global Secure Access service to the internal applications.
Reference: How to configure per-app access using Global Secure Access applications
Question: 367
Measured Skill: Design security operations, identity, and compliance capabilities (30–35%)
You have a Microsoft Entra tenant that uses Microsoft Entra ID Governance.
For each department in your company, you create a dedicated catalog and access packages to manage access to applications and data resources.
You need to ensure that team leaders in each department can perform the following actions:
- Add or remove access package assignments for the users in their department.
- Prevent the access packages from appearing in each user’s My Access
portal.
The solution must follow the principle of least privilege.
Which role should you assign to the team leaders?| A | Access Package Manager |
| B | Identity Governance Administrator |
| C | Catalog Owner |
| D | Access Package Assignment Manager |
Correct answer: DExplanation:
The Access Package Assignment Manager role is specifically designed to manage assignments to existing access packages, including viewing, adding, and removing assignments, without granting broader permissions to manage catalogs, access packages, or policies.
References:
View, add, and remove assignments for an access package in entitlement management
Delegate access governance to access package managers in entitlement management
Question: 368
Measured Skill: Design security solutions for applications and data (20–25%)
You have an Azure subscription. The subscription contains five Azure App Service instances that host public web apps. Each instance is deployed across three Azure regions.
The web apps handle sensitive customer data and must be protected from common web exploits and malicious bots.
You need to recommend a security solution that meets the following requirements:
- Provides centralized management and updates for protection rules
- Protects all the web apps without modifying the application code
- Minimizes costs
What should you include in the recommendation?| A | Azure Firewall |
| B | Azure DDoS Protection |
| C | Azure Front Door |
| D | Azure Application Gateway |
Correct answer: CExplanation:
To protect multi-region Azure App Service instances from web exploits and malicious bots while ensuring centralized rule management, the recommended solution is Azure Front Door Premium with Azure Web Application Firewall (WAF).
Global Protection & Routing: Azure Front Door is a global service that acts as a secure entry point. It natively load-balances traffic across multiple Azure regions using anycast, directing customers to the closest healthy region with the lowest latency.
Centralized Management: Instead of deploying and managing individual firewalls (like Azure Application Gateway) inside each of the three regions, you can associate a single global Azure WAF policy with your Front Door profile. This provides a single pane of glass to manage, scale, and update your security rules across all five web applications instantly.
Exploit & Bot Mitigation: The Premium tier of Azure Front Door WAF includes built-in managed rulesets (like the OWASP Core Rule Set) to defend sensitive customer data against common vulnerabilities (e.g., SQL Injection, Cross-Site Scripting). It also integrates Microsoft Threat Intelligence to detect and block malicious bots, crawlers, and scrapers before they ever reach your backend App Services.
Zero Application Modification: This architecture acts as an edge proxy network layer. It protects your applications without requiring any changes to your web application code or runtime configurations.
References:
Web Application Firewall (WAF) on Azure Front Door
Configure bot protection for Web Application Firewall
Question: 369
Measured Skill: Design security solutions for applications and data (20–25%)
You have an on-premises app that processes Personally Identifiable Information (PII) and sends the data to Azure. The app includes the following components:
- APIs that receive and send the PII
- A data ingestion pipeline that stores the PII in an Azure Data Lake Storage Gen2 account
A compliance policy requires that all the PII data be encrypted by using encryption keys that are regularly rotated and stored in a central repository.
You need to recommend a solution that adhere to the compliance policy. The solution must minimize administrative effort.
Which two components should you include in the recommendation?
(Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point)| A | Azure Cloud HSM |
| B | Microsoft Cloud PKI |
| C | Azure Key Vault |
| D | Service-side encryption (SSE) |
| E | Transparent Data Encryption (TDE) |
| F | Azure Disk Encryption |
Correct answer: C, DExplanation:
Azure Key Vault provides a centralized repository for encryption keys and supports customer-managed keys (CMKs), key rotation, and access control. Azure Storage customer-managed keys can be stored in Azure Key Vault.
Azure Storage uses Server-Side Encryption (SSE) to encrypt data at rest automatically. When combined with customer-managed keys stored in Azure Key Vault, the storage account (including Data Lake Storage Gen2) can encrypt data using organization-controlled keys without requiring application code changes.
References:
Customer-managed keys for Azure Storage encryption
Azure Storage encryption for data at rest
Question: 370
Measured Skill: Design security solutions for applications and data (20–25%)
You have an Azure subscription. The subscription contains 20 App Service web apps that provide services to external customers. Each web app has a unique certificate and key.
You need to recommend a solution to manage the keys and certificates of the web apps. The solution must meet the follow requirements:
- Provide a single tenancy to store the keys and certificates.
- Maintain FIPS 140-2 Level 3 compliance.
- Follow the principle of least privilege.
- Minimize costs.
- Minimize administrative effort.
What should you include in the recommendation?
(To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.)
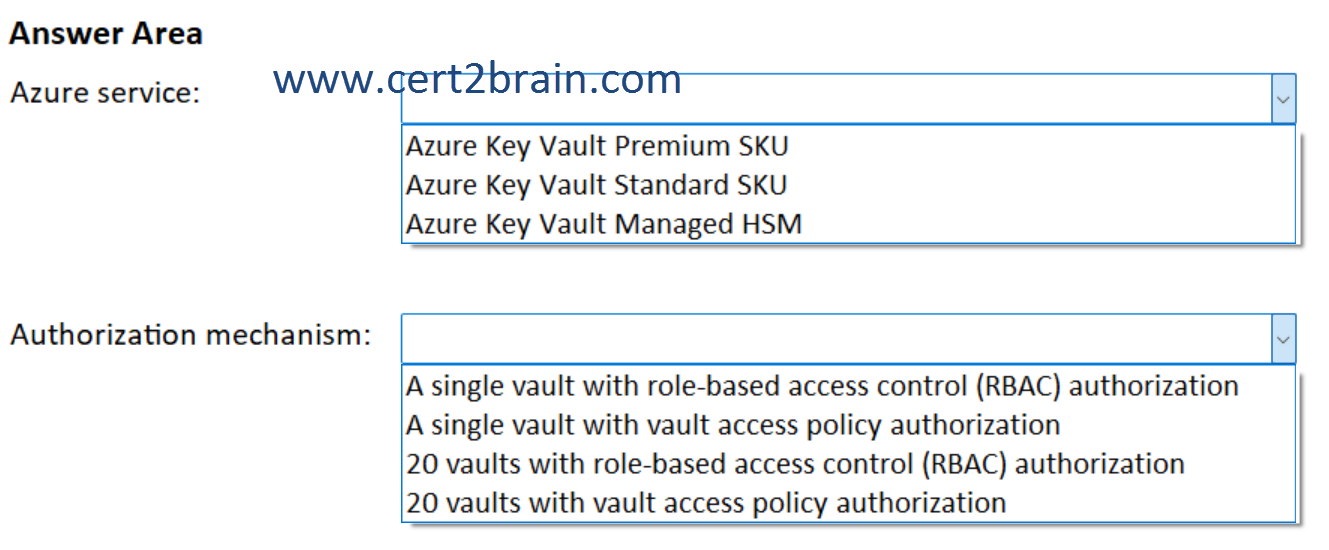
| A | Azure service: Azure Key Vault Premium SKU
Authorization mechanism: 20 vaults with role-based access control (RBAC) authorization |
| B | Azure service: Azure Key Vault Premium SKU
Authorization mechanism: A single vault with role-based access control (RBAC) authorization |
| C | Azure service: Azure Key Vault Standard SKU
Authorization mechanism: 20 vaults with role-based access control (RBAC) authorization |
| D | Azure service: Azure Key Vault Standard SKU
Authorization mechanism: A single vault with vault access policy authorization |
| E | Azure service: Azure Key Vault Managed HSM
Authorization mechanism: A single vault with role-based access control (RBAC) authorization |
| F | Azure service: Azure Key Vault Managed HSM
Authorization mechanism: 20 vaults with vault access policy authorization |
Correct answer: EExplanation:
Azure offers several solutions for cryptographic key storage and management in the cloud: Azure Key Vault (standard and premium offerings), Azure Managed HSM, Azure Cloud HSM, and Azure Payment HSM.
FIPS-140 is a US government standard with different levels of security requirements. Use the table to compare all the solutions side by side:
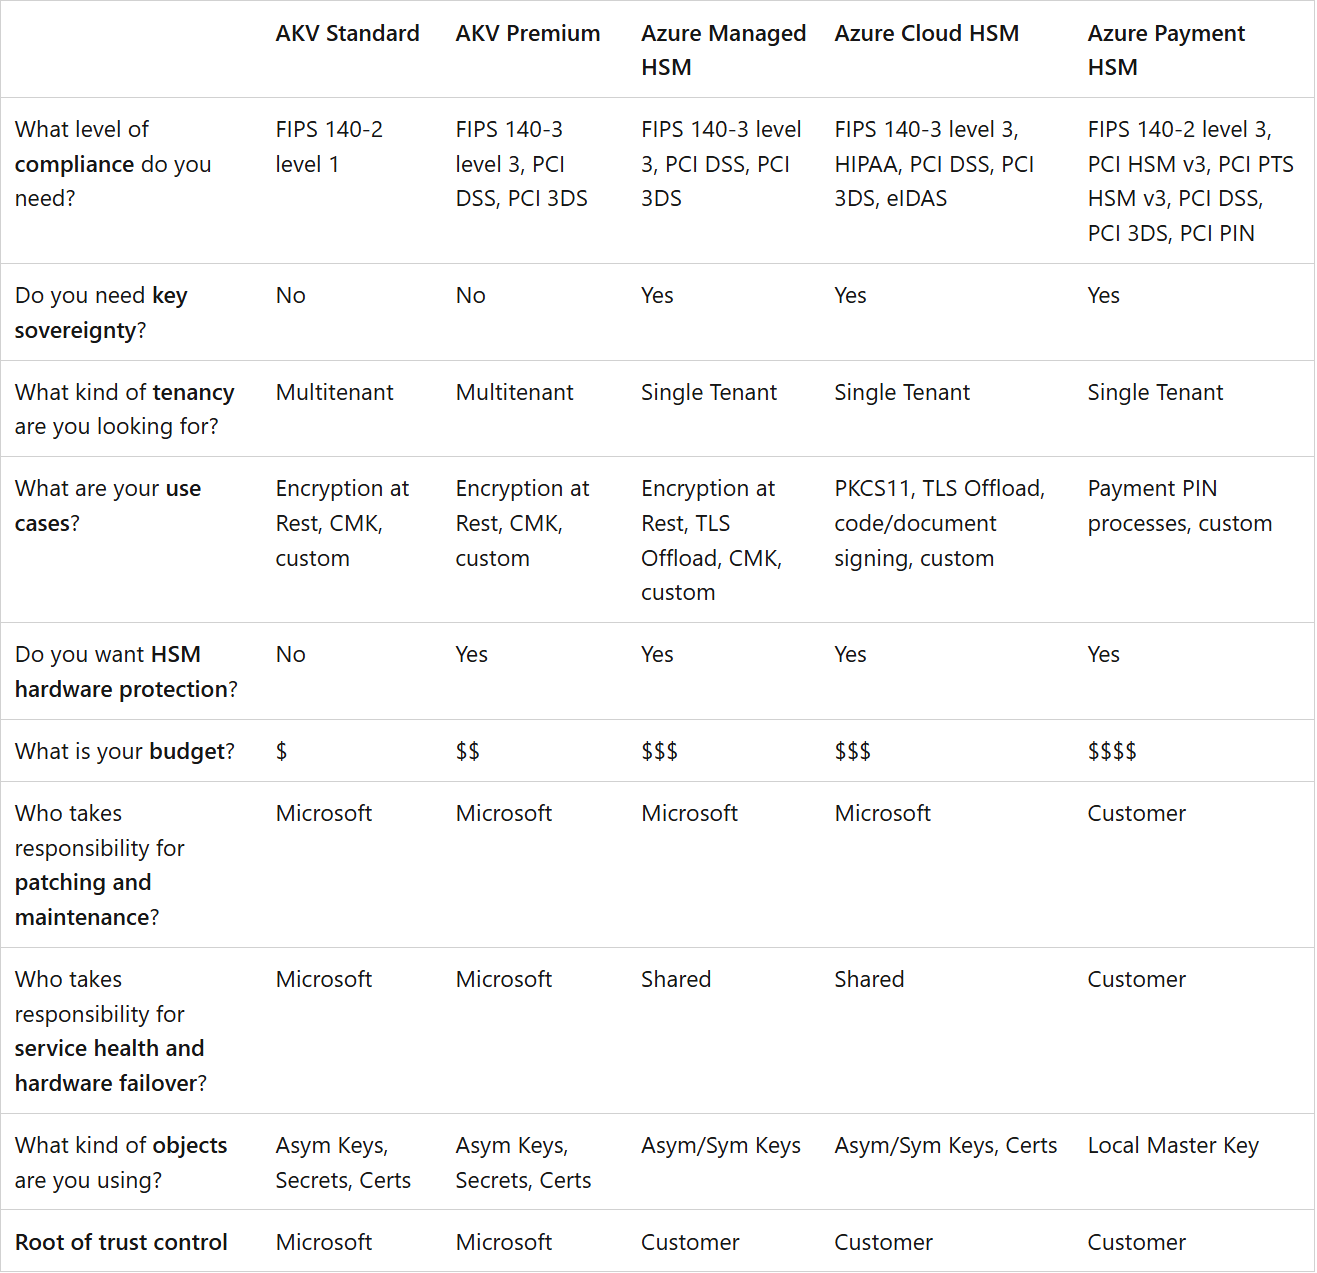
Note: Azure Key Vault Premium SKU supports HSM-protected keys, but the HSM infrastructure is multi-tenant, not single-tenant.
Azure role-based access control (Azure RBAC) is an authorization system built on Azure Resource Manager that provides centralized access management of Azure resources.
Azure RBAC allows users to manage keys, secrets, and certificates permissions, and provides one place to manage all permissions across all key vaults.
The Azure RBAC model allows users to set permissions on different scope levels: management group, subscription, resource group, or individual resources. Azure RBAC for key vault also allows users to have separate permissions on individual keys, secrets, and certificates.
References:
About keys
How to choose the right Azure key management solution
Provide access to Key Vault keys, certificates, and secrets with Azure role-based access control