Microsoft - SC-200: Microsoft Security Operations Analyst
Sample Questions
Question: 479
Measured Skill: Manage a security operations environment (20–25%)
You have a Microsoft 365 subscription.
You have a Microsoft Sentinel workspace named Workspace1 that is connected to Microsoft Defender XDR.
You have an Amazon Web Services (AWS) account named AWS1. AWS CloudTrail events are ingested into Workspace1 by using the Amazon Simple Storage Service (Amazon S3) data connector.
You have a unified incident that shows a risky Microsoft Entra sign-in followed by AWS IAM access key creation events in CloudTrail, and then a rapid increase in AWS API activity from the same identity.
You need to recommend a solution to dynamically limit the impact of similar incidents. The solution must meet the following requirements:
- Ensure that you can review and undo attack containment actions if required.
- Minimize administrative effort.
What should you include in the recommendation?| A | User and Entity Behavior Analytics (UEBA) |
| B | Automatic attack disruption in Microsoft Defender XDR |
| C | Microsoft Purview multicloud data discovery scans |
| D | Microsoft Sentinel automation rules and Azure Logic Apps playbooks |
Correct answer: BExplanation:
Microsoft has extended Automatic attack disruption to AWS-integrated scenarios. It can automatically identify compromised identities and contain AWS IAM accounts or federated users, while keeping security teams in control so that containment actions can be reviewed and reversed if necessary. This directly satisfies the requirement to dynamically limit the impact of similar incidents and to review and undo containment actions.
Additionally, automatic attack disruption is built into Microsoft Defender XDR and uses high-confidence detections and AI-driven correlation, which minimizes administrative effort compared to creating and maintaining custom automation workflows.
References:
Automatic attack disruption in Microsoft Defender
Enable attack disruption actions on AWS with Microsoft Sentinel
Question: 480
Measured Skill: Manage security threats (15–20%)
You have a Microsoft Entra tenant that has Microsoft Entra ID P1 licensing.
You have Microsoft Graph activity logs that stream to a Log Analytics workspace named Workspace1 by using the Diagnostic settings in Azure Monitor.
You can query Workspace1.
An internal line-of-business (LOB) application is suspected of enumerating Microsoft 365 groups and failing authorization checks. The application began generating a high volume of Microsoft Graph requests during the last three days, and the failures are reported as HTTP 401 and HTTP 403 errors.
You need to identify which identity is associated with the failing requests. The solution must return the top identities that generated unauthorized requests to the /groups resource during the last three days, grouped by AppId, ServicePrincipalId, and UserId.
Which KQL query should you run in Workspace1?| A | MicrosoftGraphActivityLogs
| where TimeGenerated >= ago(3d)
| where ResponseStatusCode == 200
| where RequestUri contains "/groups"
| summarize UniqueRequests=count_distinct(RequestId) by AppId
| sort by UniqueRequests desc
| limit 20 |
| B | MicrosoftGraphActivityLogs
| where TimeGenerated >= ago(30d)
| where ResponseStatusCode == 401 or ResponseStatusCode == 403
| where RequestUri contains "/users"
| summarize UniqueRequests=count_distinct(RequestId) by AppId, ServicePrincipalId, UserId
| sort by UniqueRequests desc
| limit 20 |
| C | MicrosoftGraphActivityLogs
| where TimeGenerated >= ago(3d)
| where ResponseStatusCode == 401 or ResponseStatusCode == 403
| where RequestUri contains "/groups"
| summarize UniqueRequests=count_distinct(RequestId) by AppId, ServicePrincipalId, UserId
| sort by UniqueRequests desc
| limit 20 |
| D | SigninLogs
| where TimeGenerated >= ago(3d)
| where Status.errorCode == 401 or Status.errorCode == 403
| summarize UniqueRequests=count_distinct(CorrelationId) by AppId, UserId
| sort by UniqueRequests desc
| limit 20 |
Correct answer: CExplanation:
The requirements are:
- Query Microsoft Graph activity logs - use the
MicrosoftGraphActivityLogs table.
- Last 3 days -
TimeGenerated >= ago(3d).
- Find unauthorized requests - HTTP 401 and 403.
- Target the /groups resource -
RequestUri contains "/groups".
- Group by AppId, ServicePrincipalId, and UserId.
- Return the top identities by number of unauthorized requests.
The only query that meets all requirements is:
MicrosoftGraphActivityLogs
| where TimeGenerated >= ago(3d)
| where ResponseStatusCode == 401 or ResponseStatusCode == 403
| where RequestUri contains "/groups"
| summarize UniqueRequests=count_distinct(RequestId) by AppId, ServicePrincipalId, UserId
| sort by UniqueRequests desc
| limit 20
Reference: Access Microsoft Graph activity logs
Question: 481
Measured Skill: Manage incident response (25–30%)
You have a Microsoft 365 subscription that uses Microsoft Purview.
During a suspected account compromise, an executive’s account performs Microsoft 365 Copilot
interactions.
You need to identify which Copilot interactions were performed. The solution must minimize administrative effort.
Which Microsoft Purview solution should you use?| A | Audit |
| B | eDiscovery |
| C | Data Loss Prevention (DLP) |
| D | Data Security Investigations |
Correct answer: AExplanation:
Microsoft Purview Audit is the recommended solution for identifying which Microsoft 365 Copilot interactions were performed by a user during a suspected account compromise. Audit automatically captures Copilot user interactions, including who interacted with Copilot, when the interaction occurred, and related resources accessed. No additional configuration is required beyond auditing being enabled, which minimizes administrative effort.
Reference: Audit logs for Copilot and AI applications
Question: 482
Measured Skill: Manage security threats (15–20%)
You have a Microsoft 365 subscription that uses Microsoft Defender XDR and has automatic attack disruption enabled.
During an active ransomware incident, Microsoft Defender for Endpoint automatically contains a device to limit lateral movement.
You need to use advanced hunting to return the following information:
- Devices that are contained due to response actions
- The most recent isolation state per device
How should you complete the KQL query?
(To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.)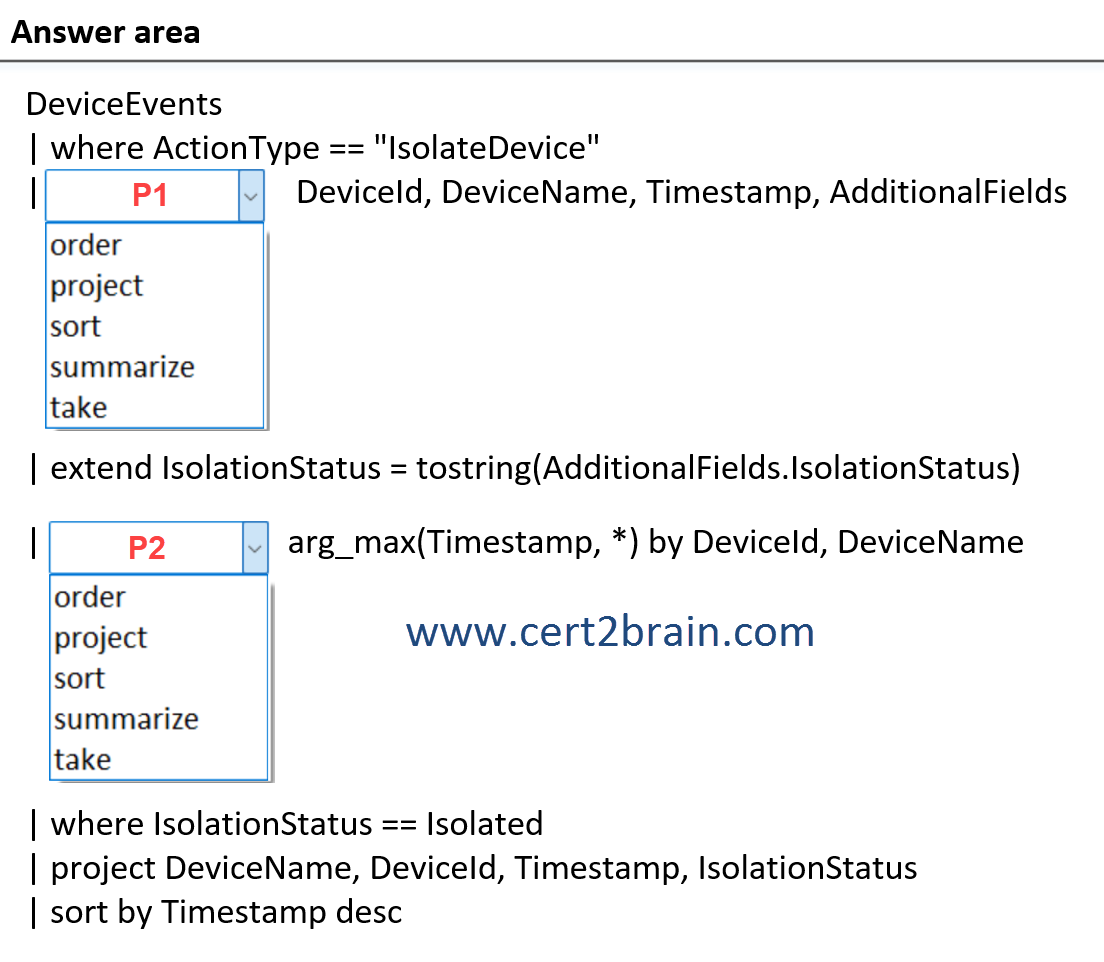
| A | P1: order
P2: project |
| B | P1: project
P2: summarize |
| C | P1: project
P2: take |
| D | P1: sort
P2: order |
| E | P1: summarize
P2: take |
| F | P1: take
P2: sort |
Correct answer: BExplanation:
The query needs to select specific columns (DeviceID, DeviceName, Timestamp, AdditionalFields) from the DeviceEvents table to pass to the next stage of the pipeline. The project operator is used in KQL to select, rename, or extend columns in the result set.
The summarize operator is the mandatory clause required to perform aggregations and group rows together in KQL. summarize arg_max(Timestamp, *) by DeviceId, DeviceName returns the most recent record for each device, satisfying the requirement to show the latest isolation state per device.
Question: 483
Measured Skill: Manage security threats (15–20%)
You have a Microsoft Sentinel workspace named Workspace1 that is connected to the Microsoft Defender portal.
You perform the following actions:
- Configure the Log Analytics workspace diagnostic setting to collect query audit data into a table named LAQueryLogs in Workspace1.
- Enable the User and Entity Behavior Analytics (UEBA) behavior layers and confirm that behavior records are being generated and stored in the SentinelBehaviorInfo and SentinelBehaviorEntities tables in Workspace1.
You need to create an advanced hunting query that meets the following requirements:
- Returns UEBA behaviors that were generated by Microsoft Sentinel during the last 24 hours
- Includes the user principal name (UPN) associated with each behavior
- Returns the behavior row, even when there is no UPN associated
How should you complete the KQL query?
(To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.)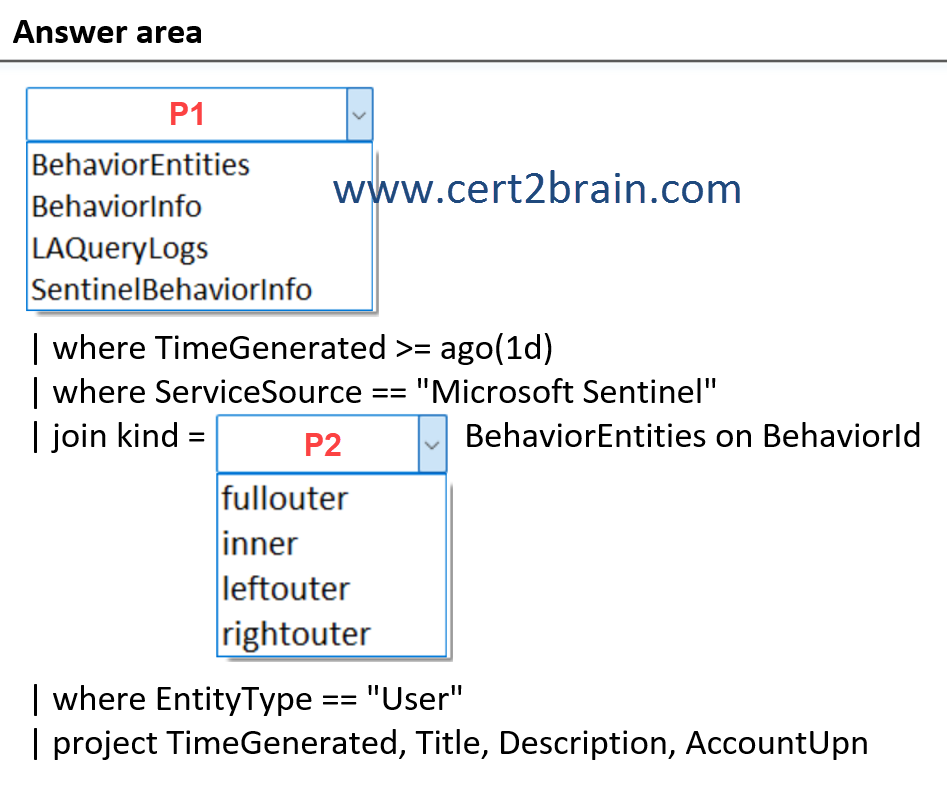
| A | P1: BehaviorEntities
P2: leftouter |
| B | P1: BehaviorInfo
P2: fullouter |
| C | P1: BehaviorInfo
P2: rightouter |
| D | P1: LAQueryLogs
P2: fullouter |
| E | P1: SentinelBehaviorInfo
P2: leftouter |
| F | P1: SentinelBehaviorInfo
P2: inner |
Correct answer: EExplanation:
SentinelBehaviorInfo contains the UEBA behavior records generated by Microsoft Sentinel, including fields such as BehaviorId, Title, and Description.
BehaviorEntities contains the entities associated with a behavior, including user entities and their AccountUpn.
The requirement states that the query must return the behavior row even when there is no UPN associated. A leftouter join returns all rows from the left table (SentinelBehaviorInfo) and matching rows from BehaviorEntities when they exist. This preserves behavior records that don't have an associated user entity.
References:
Translate raw security logs to behavioral insights using UEBA behaviors in Microsoft Sentinel
SentinelBehaviorInfo