Microsoft - SC-900: Microsoft Security, Compliance, and Identity Fundamentals
Sample Questions
Question: 271
Measured Skill: Describe the capabilities of Microsoft Entra (25–30%)
Your company uses Microsoft Entra ID.
You need to require multifactor authentication (MFA) when users sign in to Exchange Online from locations outside the corporate network.
What should you configure?| A | A Conditional Access policy |
| B | An access review |
| C | A Privileged Identity Management (PIM) role setting |
| D | A sensitivity label policy |
Correct answer: AExplanation:
Microsoft Entra Conditional Access lets you apply access controls based on conditions surrounding a sign-in. Microsoft documents Conditional Access as the recommended way to require multifactor authentication (MFA) for specific sign-in events.
For this scenario, the policy can target the appropriate Microsoft 365/Exchange Online resource and use location-related conditions to determine when the access control applies. Conditional Access supports targeting specific applications and services, including Microsoft 365 services.
References:
Microsoft Entra Conditional Access documentation
Conditional Access: Target resources
Question: 272
Measured Skill: Describe the capabilities of Microsoft Entra (25–30%)
Your company has a Microsoft Entra ID group that grants access to a financial application.
You need to ensure that group members are periodically recertified and that access is removed for members whose access is not approved.
What should you use?| A | Conditional Access |
| B | Microsoft Entra ID Protection |
| C | Azure role-based access control (RBAC) |
| D | Access reviews |
Correct answer: DExplanation:
Microsoft Entra ID Governance access reviews enable organizations to periodically review and recertify user access to groups, applications, and other resources.
Access reviews help organizations ensure that users retain access only when it is still required and approved.
In this scenario, you should configure an access review for the Microsoft Entra ID group that grants access to the financial application.
The access review can be configured to:
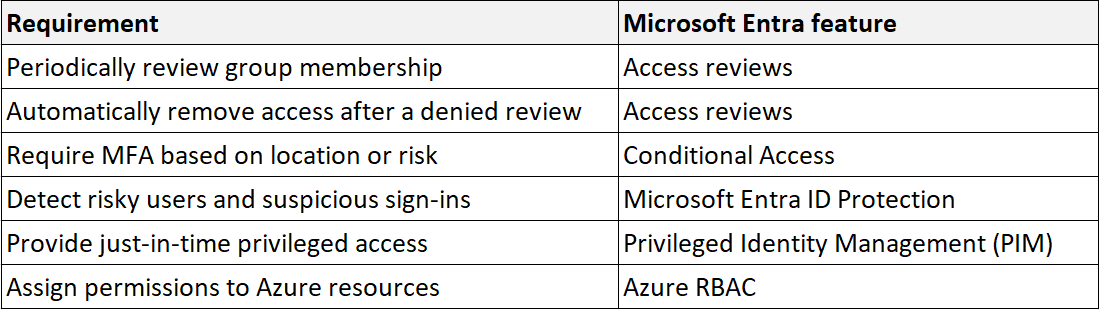
- Review group membership: Periodically verify whether users still require access to the financial application.
- Assign reviewers: Allow group owners, designated reviewers, or users themselves to review access.
- Schedule recurring reviews: Configure reviews to run weekly, monthly, quarterly, or annually.
- Require approval: Reviewers determine whether users should retain their access.
- Automatically remove access: Enable automatic application of review results so that denied users are removed from the group.
Exam Tip
For Microsoft certification exams, remember the differences between these Microsoft Entra features:
References:
What are access reviews?
Create an access review of groups and applications in Microsoft Entra ID
Question: 273
Measured Skill: Describe the capabilities of Microsoft security solutions (35–40%)
You deploy an Azure web app that must read secrets from Azure Key Vault.
You need to ensure that credentials are not stored in the app code.
Which type of identity should you use?| A | Guest user |
| B | Managed identity |
| C | Device identity |
| D | Hybrid identity |
Correct answer: BExplanation:
Microsoft specifically recommends managed identities for Azure applications that need to authenticate to resources such as Azure Key Vault without embedding credentials in application code.
A managed identity provides the Azure web app with an identity in Microsoft Entra ID whose credentials are managed by Azure. The app can use that identity to authenticate to Azure Key Vault, so developers don't have to provision, store, or rotate credentials themselves.
References:
Use managed identities for App Service and Azure Functions
Tutorial: Use a managed identity to connect Key Vault to an Azure web app in .NET
Question: 274
Measured Skill: Describe the capabilities of Microsoft Entra (25–30%)
Your company is evaluating the use of Microsoft Entra ID Protection.
What is a use case of Microsoft Entra ID Protection?| A | The detection of vulnerabilities that affect user accounts |
| B | The enforcement of compliance requirements for devices |
| C | The protection of on-premises identities |
| D | The calculation of a Microsoft Secure Score for devices and security configurations |
Correct answer: AExplanation:
Microsoft Entra ID Protection helps organizations detect, investigate, and remediate identity-based risks.
It uses Microsoft's threat intelligence and machine learning to identify potentially compromised user accounts and suspicious sign-in activities.
Microsoft Entra ID Protection provides three primary capabilities:
- Risk detection: Identifies suspicious activities, such as leaked credentials, unfamiliar sign-in properties, and malicious IP addresses.
- Risk investigation: Enables administrators to investigate risky users and risky sign-ins.
- Risk remediation: Supports automated responses, such as requiring multifactor authentication (MFA) or a secure password change.
References:
What is Microsoft Entra ID Protection?
What are risk detections?
Question: 275
Measured Skill: Describe the capabilities of Microsoft Entra (25–30%)
You have a Microsoft 365 subscription.
You need to recommend a solution for assigning administrative permissions to users. The solution must meet the following requirements:
- The users must request administrative permissions when they need them.
- The administrative permissions must be active for a maximum of three hours.
What should you include in the solution?| A | Compliance Manager |
| B | Conditional Access |
| C | Privileged Identity Management (PIM) |
| D | Microsoft Defender for Identity |
Correct answer: CExplanation:
Microsoft Entra Privileged Identity Management (PIM) provides just-in-time, time-based privileged access. Users with eligible role assignments can request activation when they need privileged access.
For this scenario, PIM directly satisfies both requirements:
Request permissions when needed: PIM supports role activation and can require approval before a privileged role is activated.
Maximum three-hour activation: PIM provides an Activation maximum duration setting. Microsoft states that this controls how long an activated role assignment remains active before it expires, with configurable values from 1 to 24 hours. Therefore, it can be configured for 3 hours.
References:
Activate my Azure resource roles in Privileged Identity Management
Configure Microsoft Entra role settings in Privileged Identity Management